Dynamo AI for Financial Services

Productionize High-Impact AI Without Surrendering Control

Dynamo AI helps banks, insurers, and fintechs deploy secure, reliable generative and agentic AI across customer and enterprise workflows. Evaluate risk, enforce policy, and maintain control from testing through production.

See Dynamo AIΒ in action

The AI Control Gap

AI systems can expose customer data, hallucinate advice or policy details, violate internal or regulatory requirements, and take destructive actions through connected tools.

What legacy security can’t see

Model

Behavior & outputs

not evaluated

Interaction

Prompts, responses & retrieved context

not inspected

Agent
Tool calls, APIs & MCP actions

not governed

The AI-specific control layer

Evaluate Β· Inspect Β· Govern

Use Cases

Protect AI across high-impact customer, risk, and enterprise workflows

Model, Application, and Third-Party Assurance

  • Evaluate commercial, open-source, fine-tuned, and vendor-provided models.
  • Benchmark accuracy, hallucination, robustness, security, and policy adherence.
  • Generate evidence for model selection, validation, approval, and ongoing oversight.

Customer, Policyholder, and Workforce AI

  • Govern chat, RAG, call-center copilots, virtual agents, knowledge assistants, and policy or claims-support workflows.
  • Detect hallucinations, unsupported claims, prohibited advice, prompt attacks, and policy violations before they reach users.
  • Escalate sensitive or high-impact interactions for human review.

Sensitive Data and Information Controls

  • Detect and prevent exposure of PII, account details, payment data, claims data, and enterprise secrets.
  • Enforce data-use, jurisdiction, retention, and information-handling rules in the application layer.
  • Preserve approved access to knowledge without creating new data-loss pathways.

Agentic Workflows and AI-Enabled Development

  • Map risk across agents, tools, permissions, files, APIs, and MCP servers.
  • Monitor code, shell, data, and tool activity in real time.
  • Block, scope, or route high-risk actions for human approval before execution.

AI Risk Management and Governance

  • Translate internal policies, risk appetite, and regulatory obligations into measurable tests and enforceable controls.
  • Maintain continuous evidence as models, vendors, data, and workflows change.
  • Provide shared visibility for product, engineering, cybersecurity, compliance, risk, and audit teams.

Business Impact

Put AI into production faster, and stay able to defend it

01
Clear the approval bottleneck: pre-approved policy replaces case-by-case legal review.
02
Lower the cost of running controls with efficient, low-latency guardrails.
03
Identify model, application, and third-party risk before deployment.
04
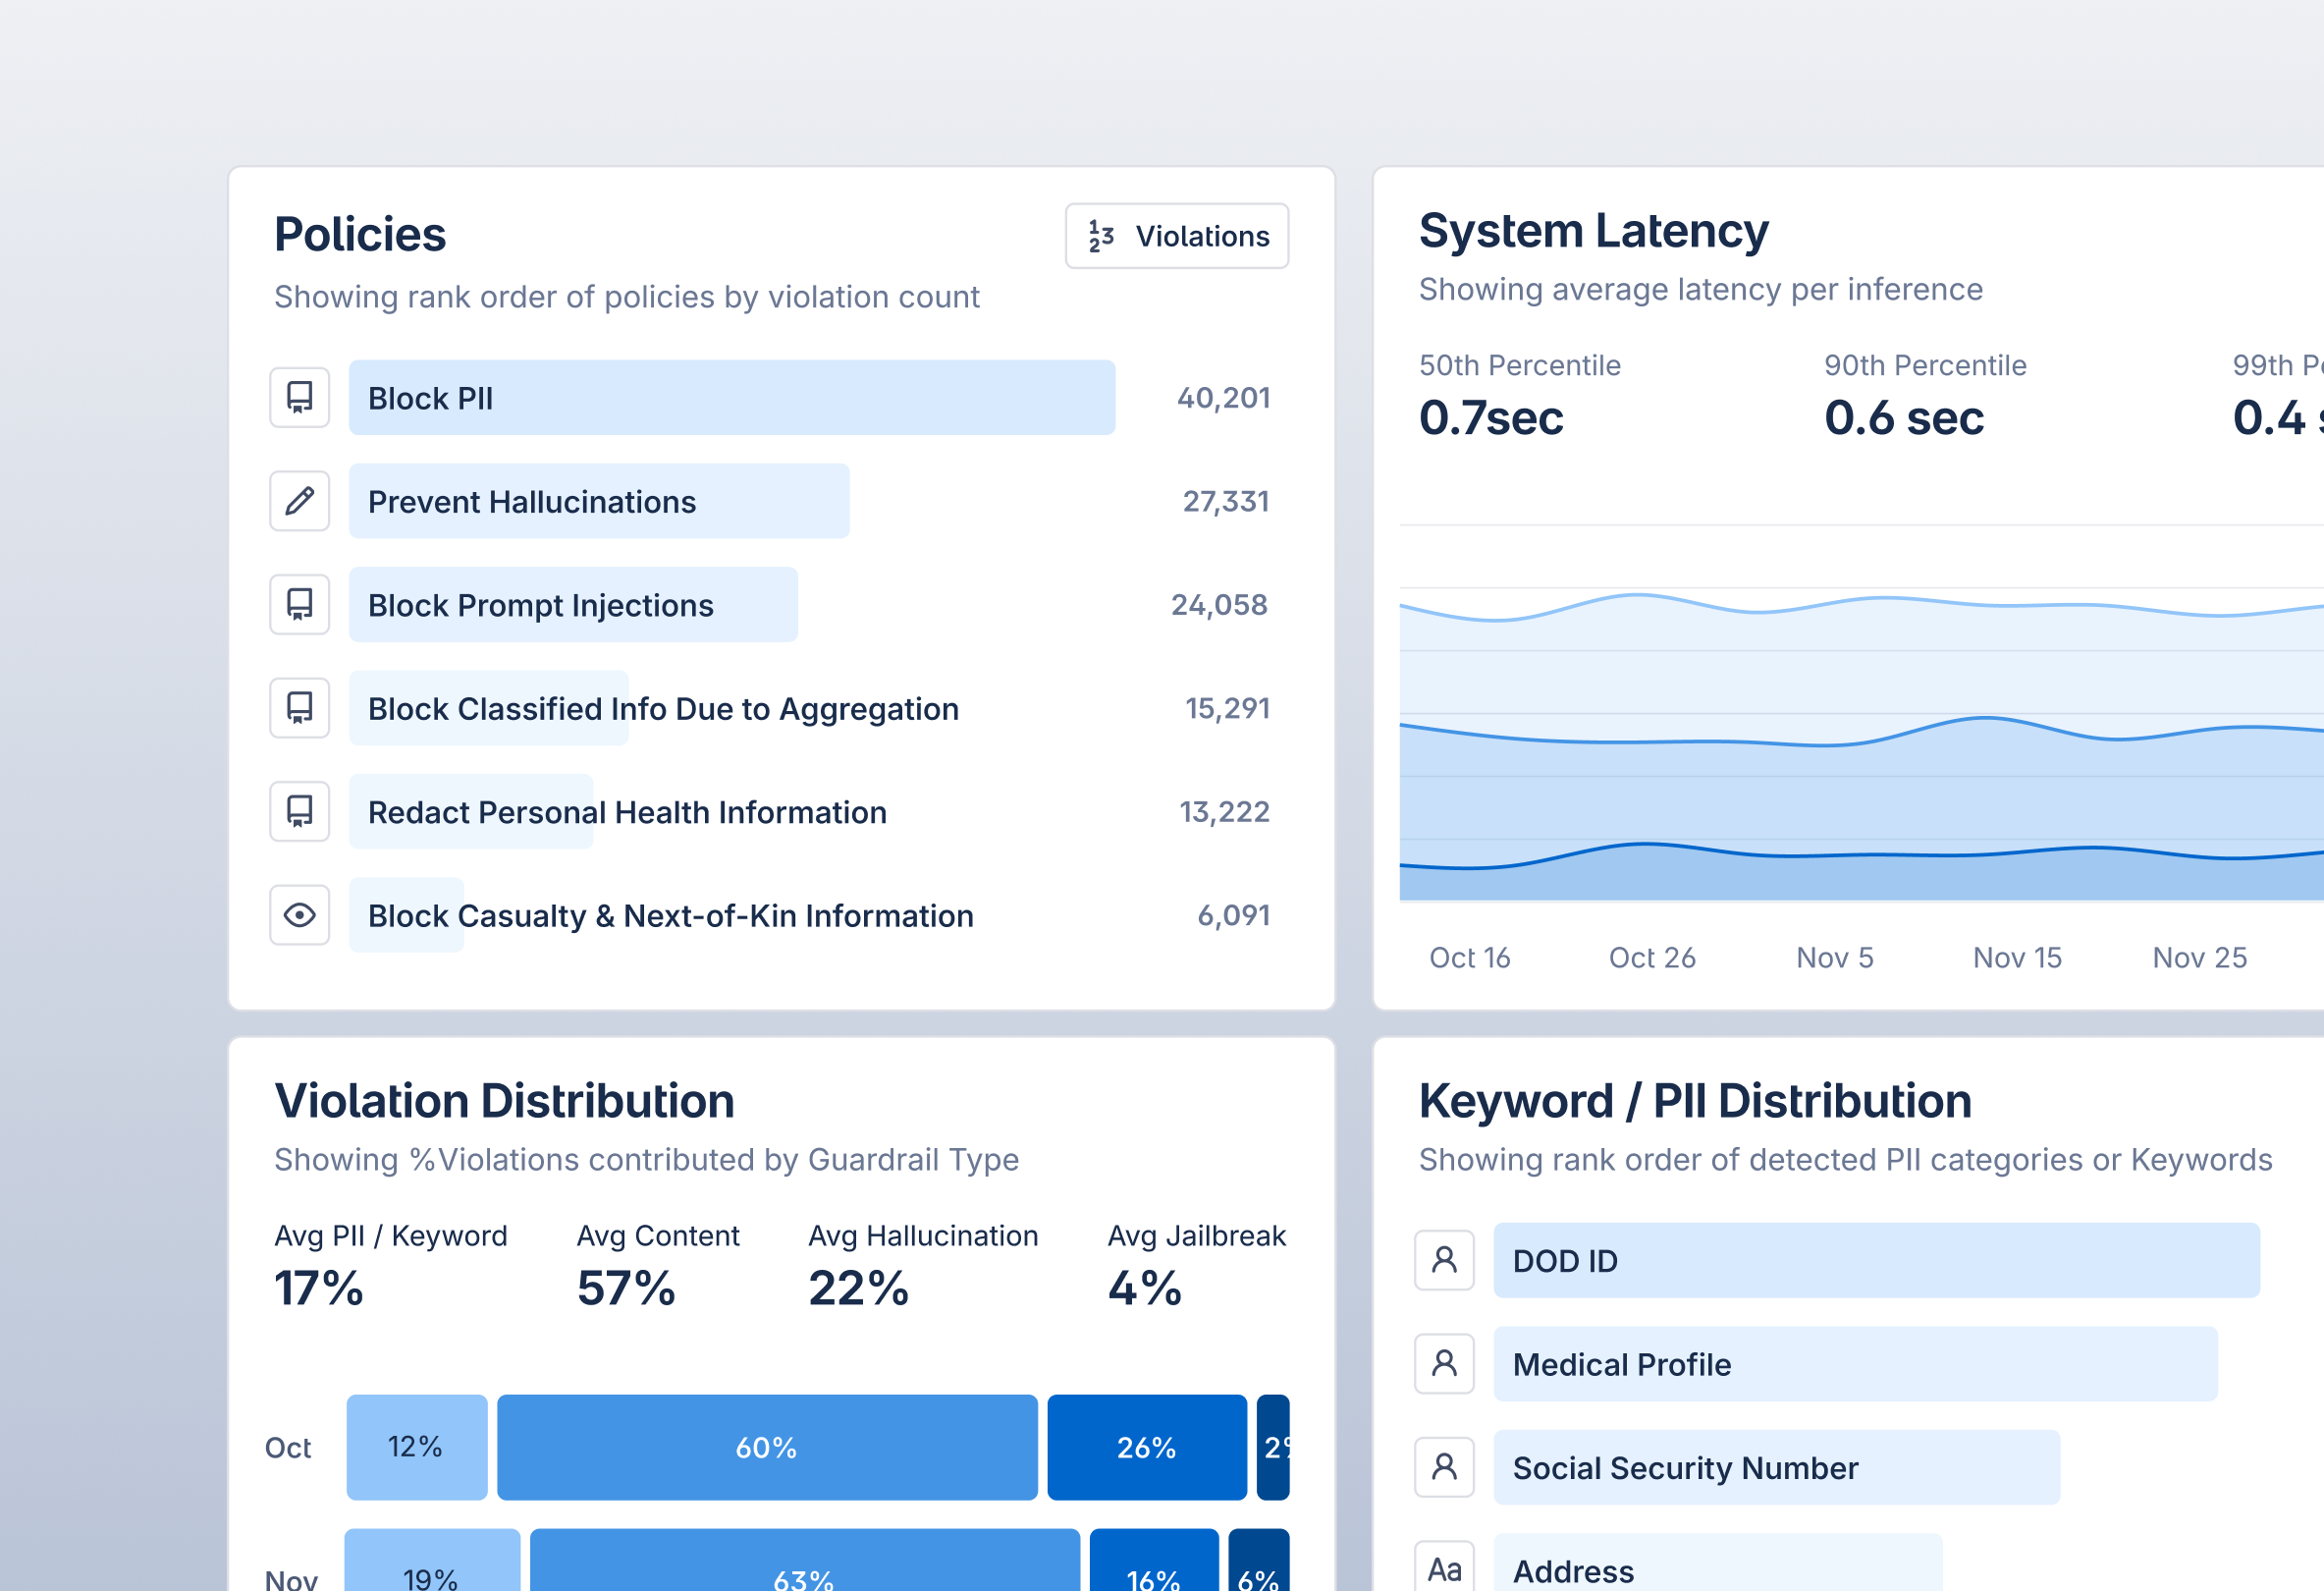
Stop attacks, hallucinations, and policy violations in the request path.
05
Protect customer and proprietary data across every AI workflow.
06
Govern agent tool calls, credentials, and destructive actions at the point of execution.
07
Maintain continuous visibility and audit-ready evidence across teams and use cases.
08
Scale governance to new business units and regions without rebuilding it each time.

Capabilities

Evaluate AI with confidence. Protect every interaction. Keep agents under control.

Red-Team, Performance, & Compliance Evaluation

Test how AI performs against your institution’s policies, business needs, and risk tolerances before and after deployment.

Model Selection & Validation

  • Compare commercial, open-source, and fine-tuned models
  • Benchmark accuracy, reliability, and policy adherence
  • Evaluate vendor-provided models and applications
  • Validate changes before production rollout

Financial Workflow Testing

  • Test customer, underwriting, and claims workflows
  • Identify hallucinations and unsupported financial advice
  • Probe prompt attacks and sensitive-data leakage
  • Measure failures against institutional risk thresholds

Expert Review & Refinement

  • Define success with business and risk teams
  • Review findings with subject-matter experts
  • Escalate ambiguous or high-impact results
  • Improve evaluations through reviewer feedback

Evidence for Approval & Oversight

  • Produce explainable results for model validation
  • Connect findings to tests and policy criteria
  • Document gaps and remediation priorities
  • Track performance as systems change
Learn More

Real-Time Controls, Protection, & Observability

Apply institutional policy to live AI interactions, protecting sensitive information and keeping communications within approved boundaries.

Institution-Specific Guardrails

  • Start with 150+ out-of-the-box guardrails
  • Define privacy, advice, and communication boundaries
  • Turn internal policies into custom controls
  • Adapt protections across products and workflows

Interaction & Data Protection

  • Inspect prompts, responses, and retrieved content
  • Detect customer, account, and payment-data exposure
  • Identify prompt injection and jailbreak attempts
  • Flag unsupported claims and policy violations

Enforcement at Production Scale

  • Block, redact, sanitize, warn, or route
  • Apply consistent controls across AI applications
  • Escalate sensitive interactions for human review
  • Keep controls efficient and low latency

Visibility & Continuous Improvement

  • Explain policy decisions and enforcement actions
  • Monitor violations across customer and workforce AI
  • Tune guardrails with fully on-premises RLHF
  • Improve performance and reduce false positives
Learn More

AI Agent Security & Control

Control what AI agents can access and execute across financial workflows, enterprise operations, and software development.

Agent Risk Discovery

  • Map tools, files, APIs, permissions, and MCP
  • Identify dangerous combinations of agent capabilities
  • Trace attack paths across connected tools
  • Prioritize risks before agents reach production

Access & Scope Control

  • Find unused or excessive tool access
  • Reduce permissions to fit intended tasks
  • Limit unnecessary access to sensitive information
  • Apply least privilege across agent workflows

Action-Level Enforcement

  • Check policy before tool calls execute
  • Allow, deny, or require human approval
  • Govern shell, file, API, and tool activity
  • Block unauthorized or destructive actions

Ongoing Agent Oversight

  • Monitor agent trajectories and policy violations
  • Detect anomalous or high-risk behavior
  • Reassess risk as tools and permissions change
  • Maintain records of agent actions and decisions
Learn More

Deployment & Integration

Bring evaluation and control into your existing AI infrastructure, from initial pilots to enterprise production.

Infrastructure Choice

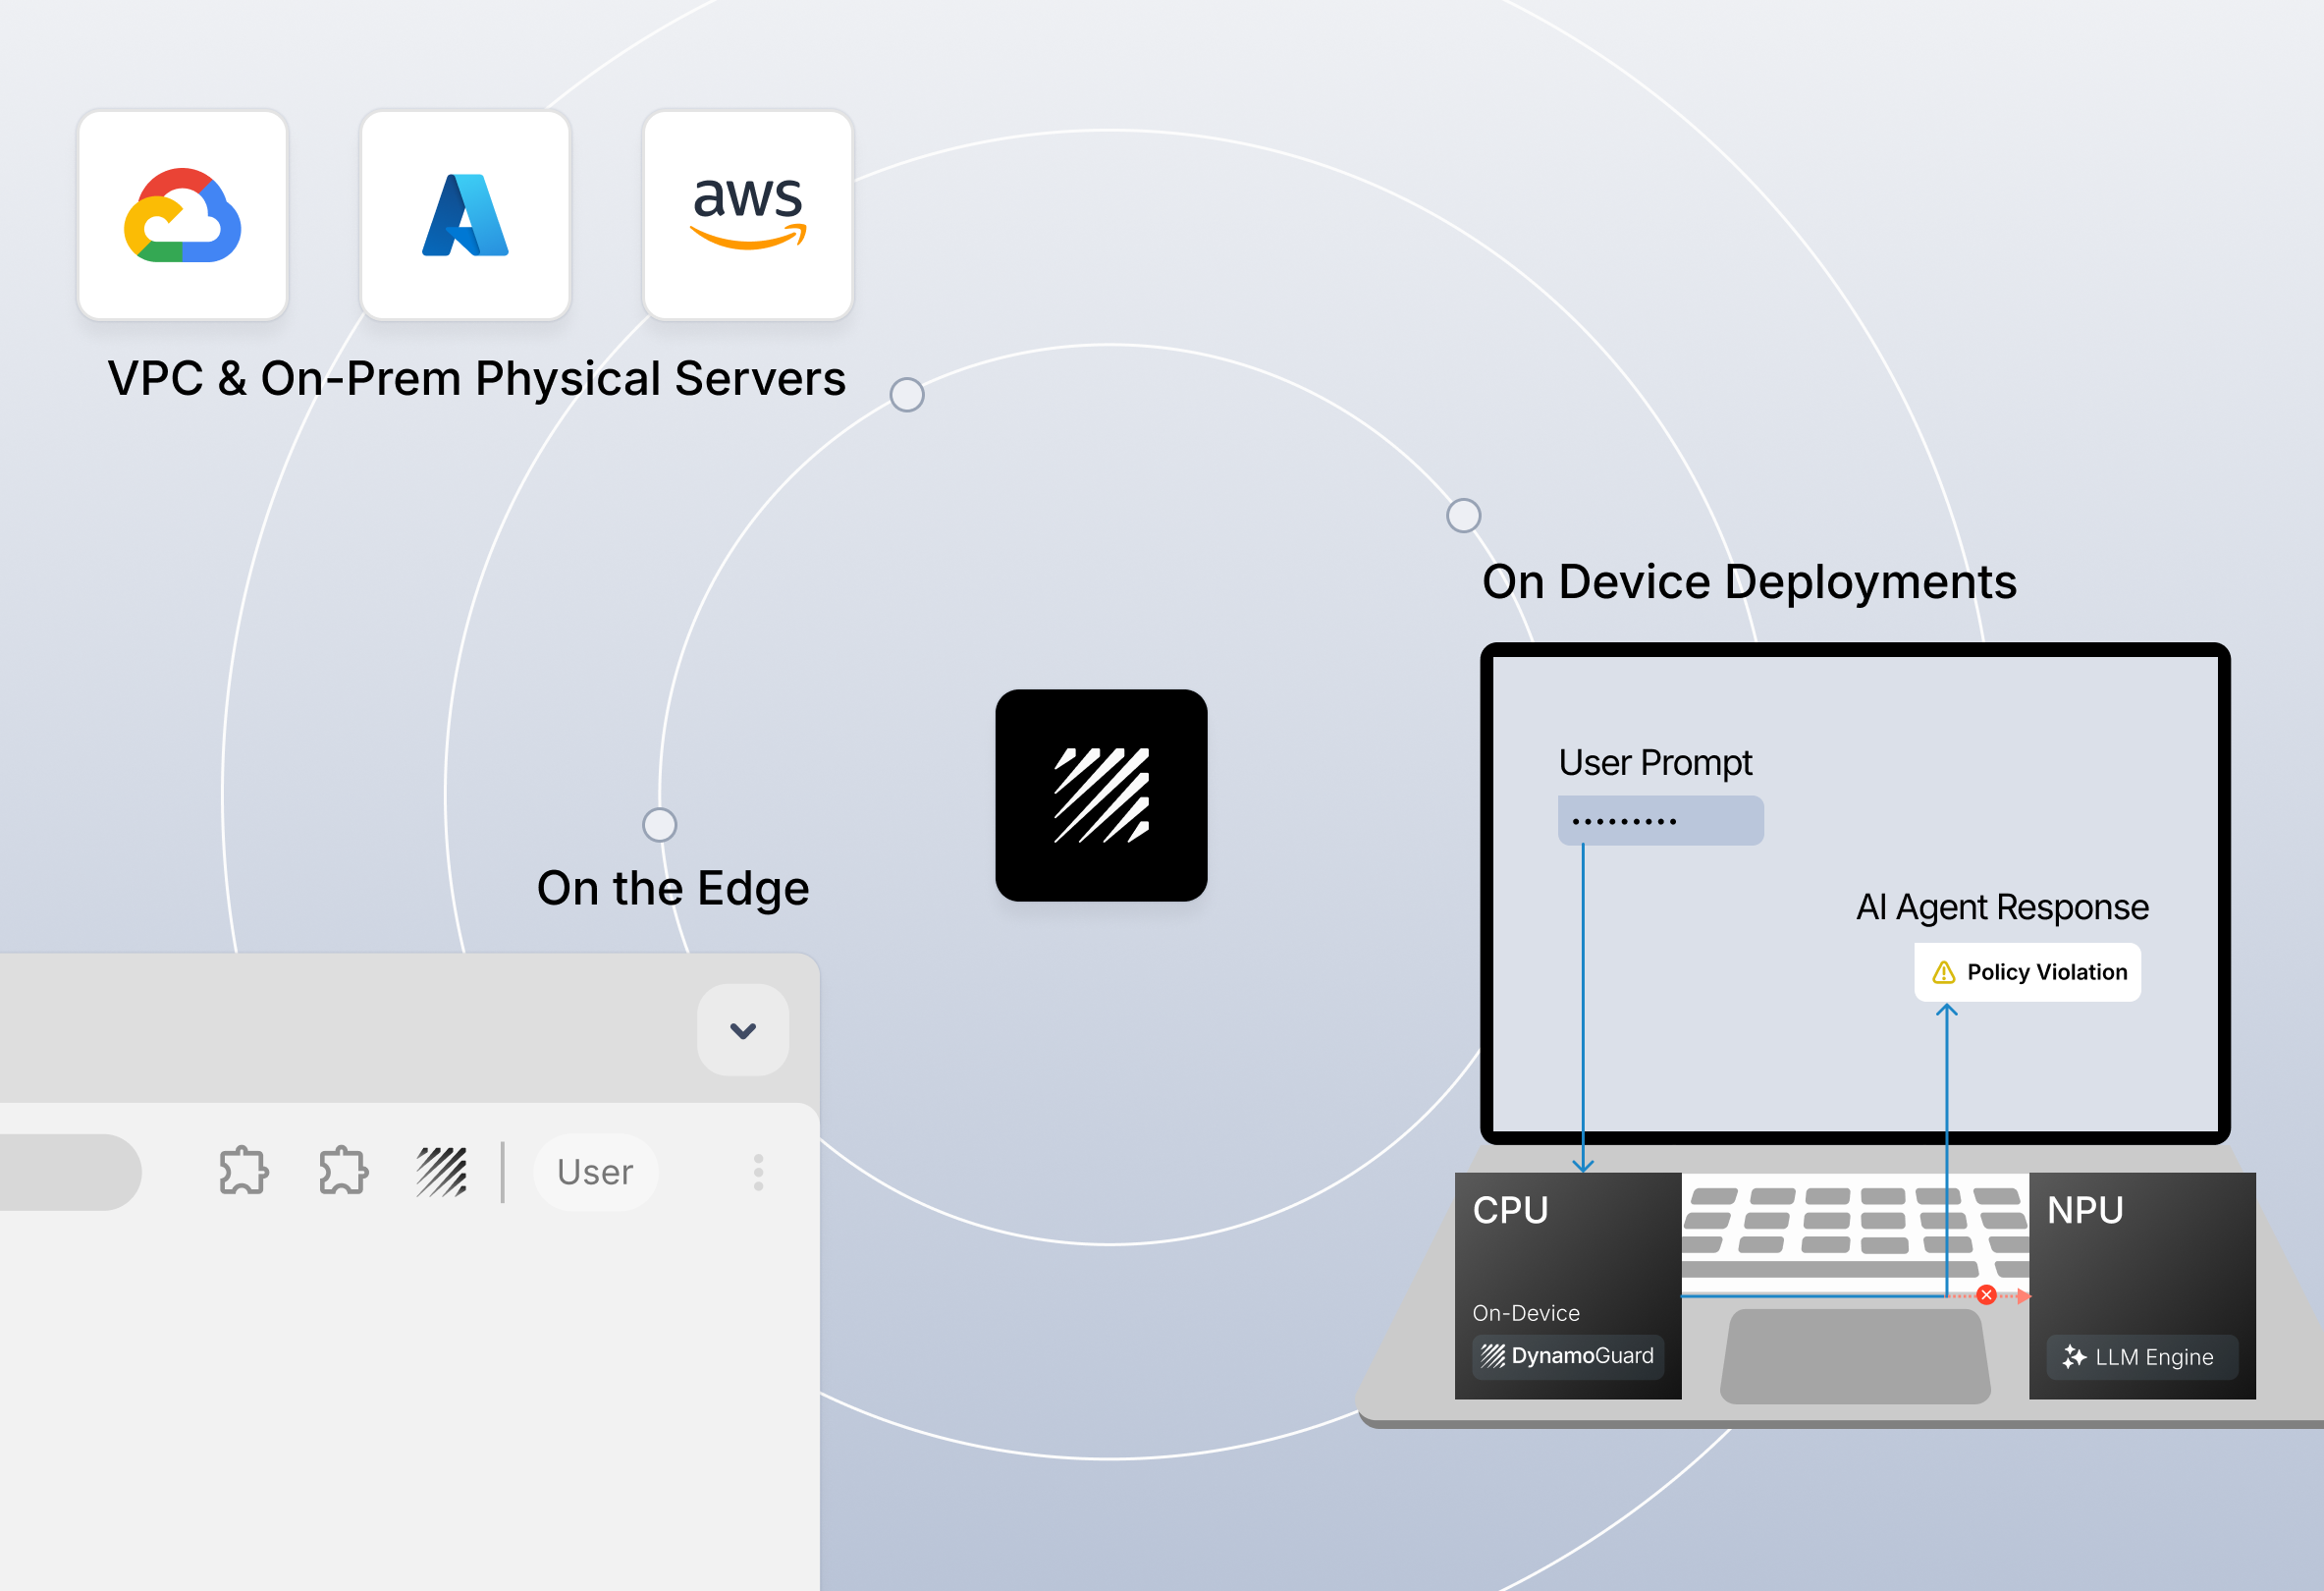
  • Deploy in cloud, VPC, or hybrid environments
  • Run on-premises or at the edge
  • Operate within institutional security boundaries
  • Expand as adoption and workloads grow

Model & Provider Flexibility

  • Support commercial and open-source models
  • Evaluate fine-tuned and institution-specific models
  • Protect copilots, applications, and AI agents
  • Maintain controls as providers and versions change

Application & Development Integration

  • Connect through APIs and AI gateways
  • Protect chat, RAG, and copilot workflows
  • Embed evaluations into CI/CD pipelines
  • Integrate with existing enterprise systems

Agent & Tool Integration

  • Connect agent frameworks and MCP servers
  • Integrate through client hooks and network proxies
  • Govern access to tools, files, and APIs
  • Work with existing network security infrastructure
Learn More

Why Dynamo?

One control layer your security, risk,
and engineering teams can share

From Policy to Enforcement
in One Workflow

Risk, compliance, and legal define policy in plain language. Dynamo versions it, tests it, and enforces it in production, all from a single pane of glass

Guardrails Proven on Production Traffic

Purpose-built models, not general-purpose LLM judges. Fast and affordable enough to run inline at the scale of global financial institutions.

Coverage Across the
Full AI Surface

Protect the model, application, data, and agent action, including the tools, MCP servers, and credentials agents reach for at runtime.

Evidence as a By-Product

Every decision carries its lineage: policy version, clause violated, action taken. Mapped to the control frameworks your auditors and regulators already use.

Deploys on Your Terms

Any model, any provider, any environment: cloud, on-premises, or air-gapped, inside your own perimeter. Start with one use case, extend to many.

Productionize
AI with confidence

Deploy generative and agentic AI with the evidence, controls, and visibility your institution needs.

Build Your AIΒ Control Strategy
Productionize Gen AI faster
with Dynamo AI

By submitting this form, you acknowledge that your information will be processed for communication and support purposes. See our Privacy Policy for details.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Your Contact Information
Share your contact details to get started
Book a Demo
Talk to a Dynamo AI Expert to discuss your Gen AI challenges
Download your Playbook

By submitting this form, you acknowledge that your information will be processed for communication and support purposes. See our Privacy Policy for details.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Your Contact Information
Share your contact details to get started
Download Document
Get Dynamo AI’s expert opinion on current issues